Cubic

Cloudflare for agent actions.

Your Fable 5 can't escape the cube

VIEW NETWORK
1,842
AGENTS ONLINE
24,921
INTENTS EVALUATED
23,884
ALLOWED
123
ESCALATED

AI agents are gaining access to everything codebases, infrastructure, money with credentials they can leak and authority they were never meant to hold. Cubic sits between agents and their tools. Every tool call becomes an intent, evaluated against identity, policy, and live trust context then allowed, denied, or escalated. Agents receive scoped, expiring capabilities, never raw keys. We authorize. Existing tools execute. Every decision is recorded.
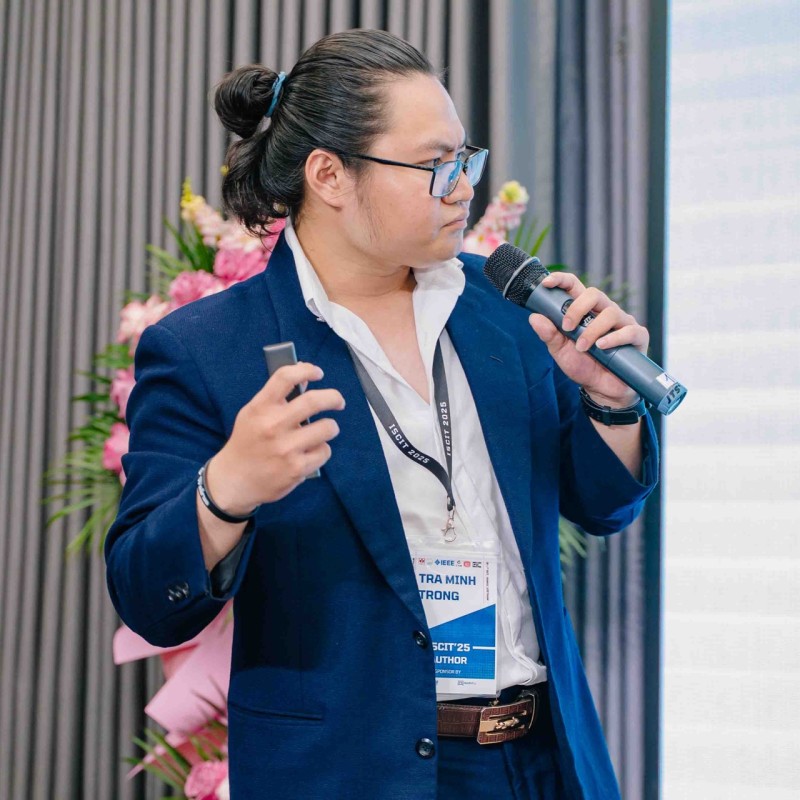
tron.jpeg
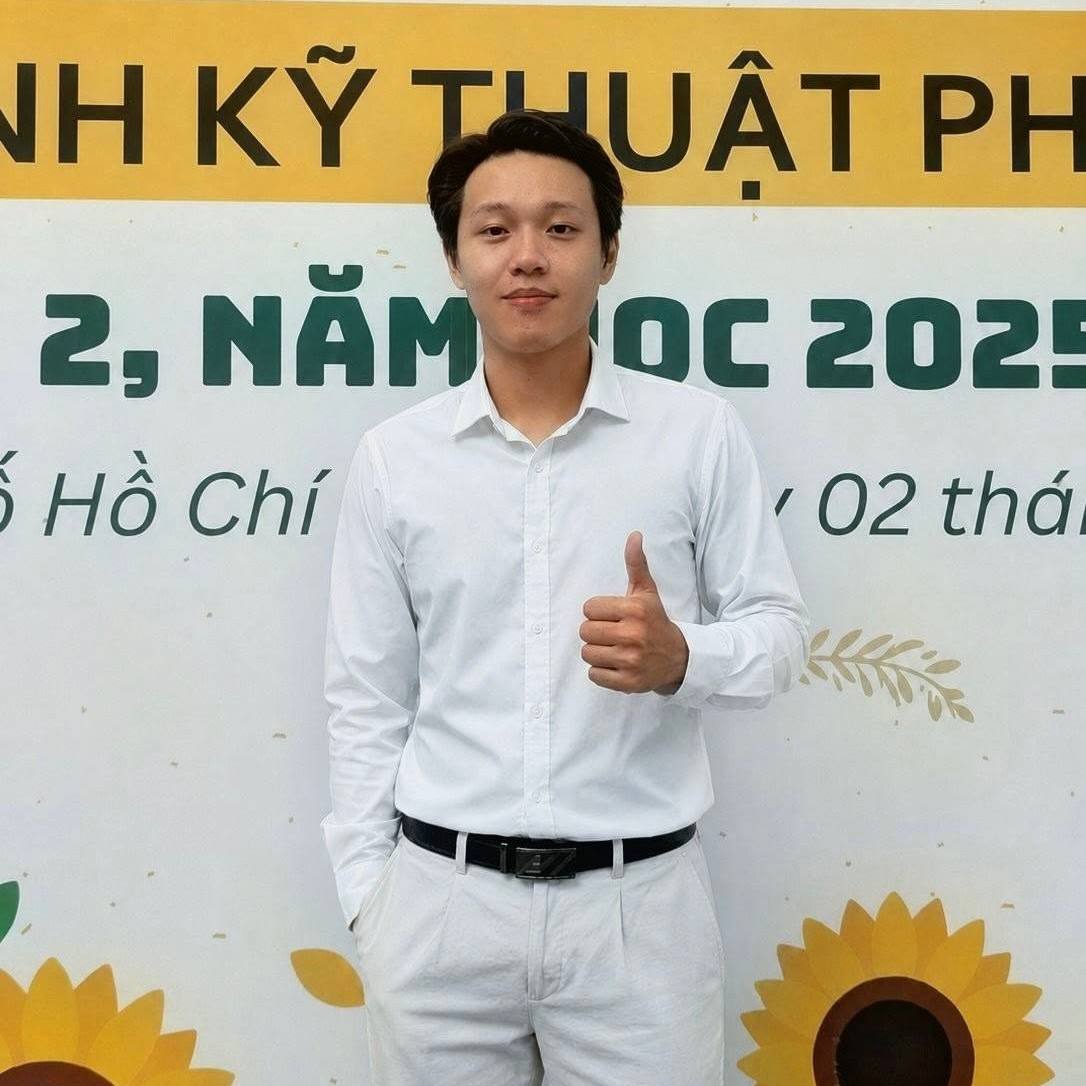
min.jpeg

From the former Web3 engineers behind centralized-exchange infrastructure — systems where one leaked key is a lost company — with research published on ERC-8004 and onchain agent identity. We spent years guarding the keys. Now we're building the layer that means agents never hold them.

THE GRAPHHEDERALEDGERERC-8004AGENT0BLOCKY402MCP

THE PRODUCT

Every call, interrogated.

01 / THE GATE

What does Cubic do?

Every agent tool call is intercepted and normalized into an intent — who is calling, what action, on which resource. A deterministic policy engine evaluates it against identity, context, and tenant rules, then answers one of three things: allow, deny, or escalate. On allow, the agent gets a scoped, expiring capability — never a reusable API key.

>Normalizes any tool call into a structured intent
>Deterministic ALLOW / DENY / ESCALATE — never an LLM guess
>Scoped, expiring capabilities instead of raw credentials
>Existing MCP servers and executors keep doing the execution
02 / TRUST CONTEXT

How are risky calls judged?

Decisions draw on live context: the agent's ERC-8004 identity and reputation, validation records indexed by The Graph's Agent0 subgraphs, recent activity, and resource sensitivity. Low-risk calls flow autonomously. High-risk ones — production deploys, fund movements — pause for hardware-backed approval through Ledger before proceeding.

>ERC-8004 identity, reputation & validation via The Graph
>High-risk actions require Ledger hardware approval
>Prompt-injection attempts hit the policy wall and get DENY
>Every intent → decision → capability → result is recorded
03 / MACHINE PAYMENTS

How do agents pay for tools?

When an agent needs a paid service — a security scan, an inference call — the invoice is treated as one more action to authorize. The gateway checks the tenant's spend policy: is the service allowlisted, is the amount within budget, does the agent's reputation clear the bar? Approved payments settle over x402 on Hedera, and the receipt joins the same auditable chain.

>402 invoices normalized into payment intents
>Per-task budgets, service allowlists, reputation thresholds
>Settlement over x402 on Hedera via the Blocky402 facilitator
>Receipts recorded alongside every other agent action

THE GATEWAY

Every call, decided in the open.

GATEWAY — LIVE DECISIONS
SIMULATED FEED — DEMO NETWORK

WHY NOW

The bill for trusting agents is already due.

Put your agents inside the cube.

Connect a wallet to open your tenant console — register agents, write policies, and watch every tool call get interrogated.

READ DOCS